An agent that is read-only by default
The agent runs in your cluster with a ClusterRole limited to the get, list and watch verbs. It reads nodes, pods, namespaces, volumes and workloads, along with node metrics. Without the actions mode, it has no write permission.
Its pod meets the restricted level of the Pod Security Standards: non-root user, immutable root filesystem, all capabilities dropped, no privilege escalation and seccomp RuntimeDefault. The agent token stays in a Secret that you create: the kubelet mounts it, and the agent reads no Secret through the API.
What leaves your cluster, and what does not
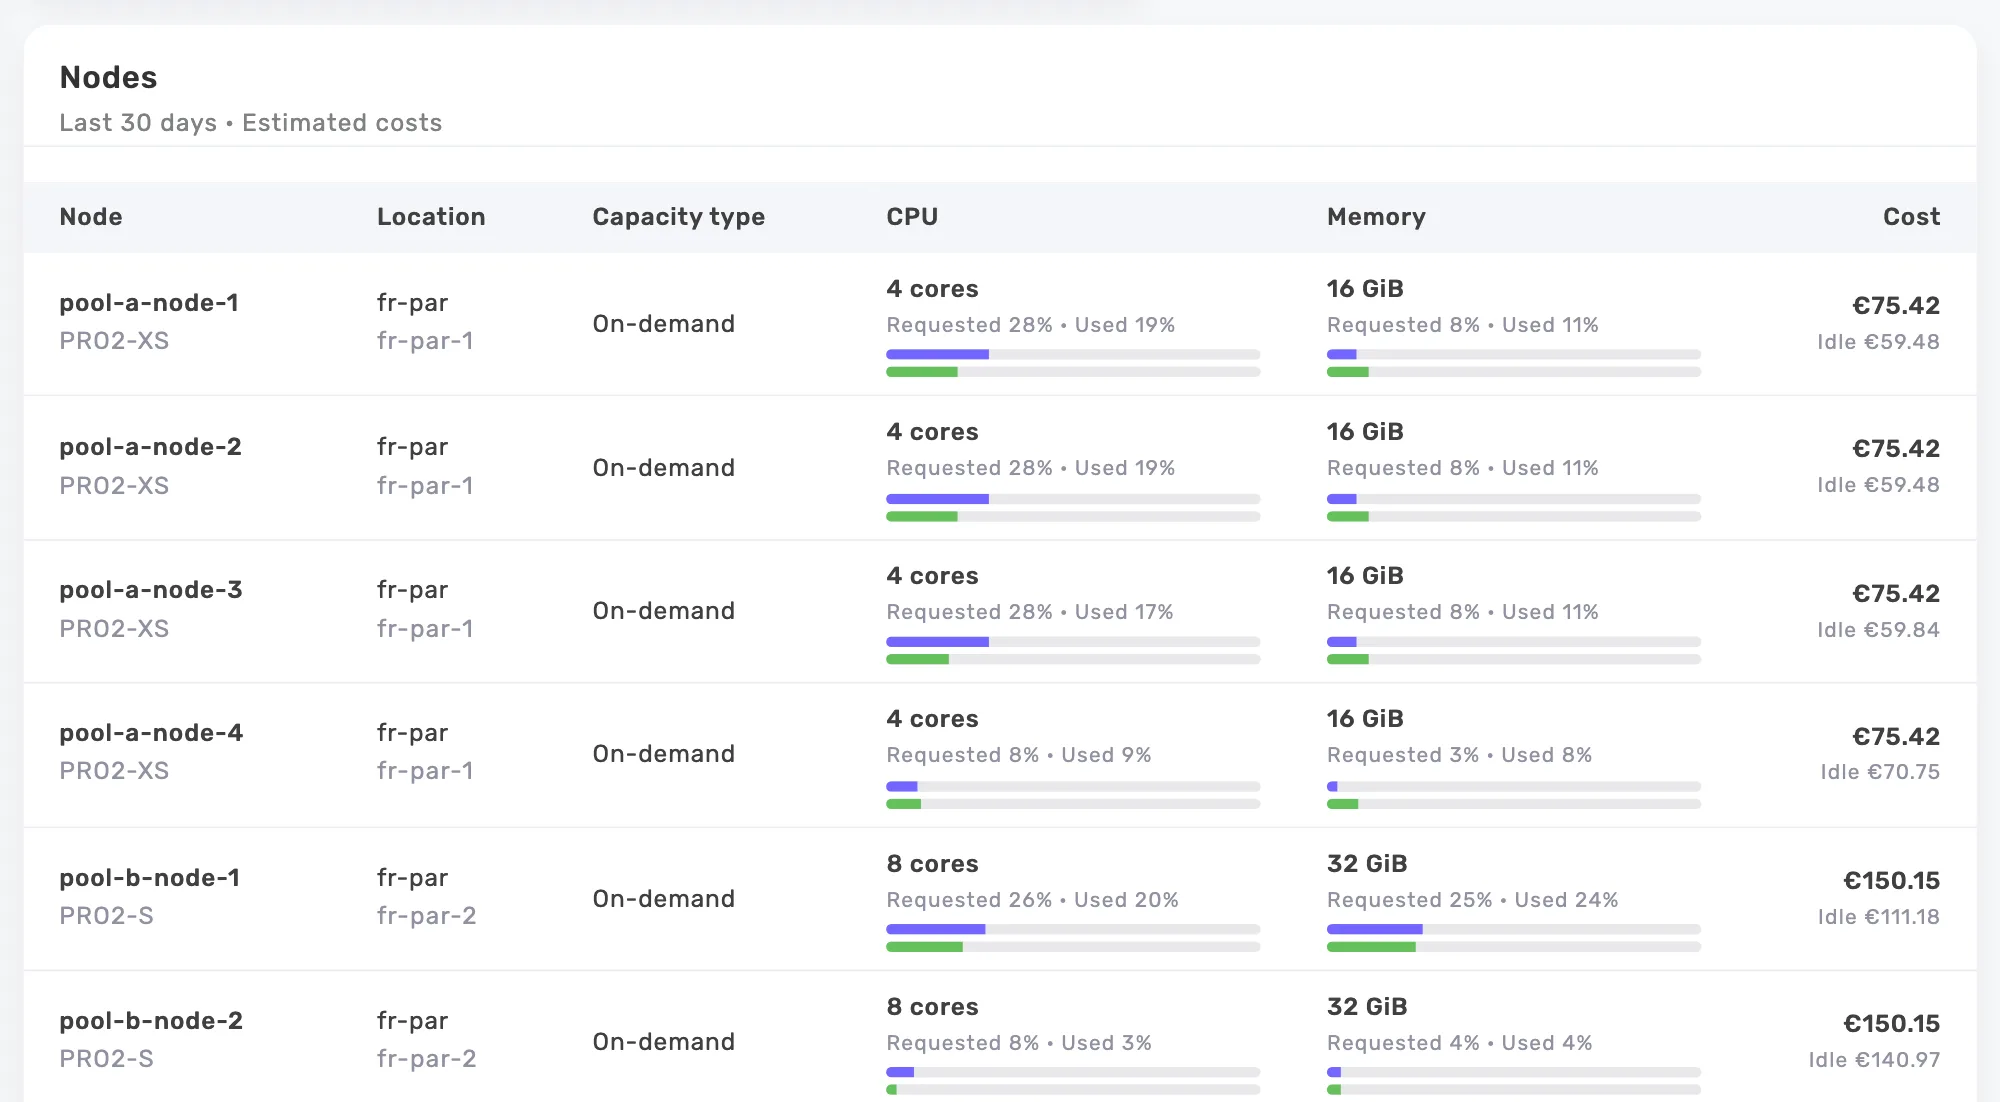
Onicost receives the inventory of the cluster and the usage of its containers. Nothing more is needed to compute your costs and recommendations.
- Sent: nodes, namespaces, workloads with their labels, requests and limits, CPU and memory usage of each container.
- Never collected: Secrets, ConfigMaps, logs, application data and traffic.
- Under your control: exclude.namespaces drops whole namespaces, exclude.labelKeys removes label keys before sending.
Actions only if you enable them
The scheduler needs dedicated permissions to stop an environment. They are granted only if you install the chart with actions.enabled=true, and the ClusterRole then adds the patch verb on Deployments, StatefulSets, CronJobs and HorizontalPodAutoscalers.
The agent writes the original values to an annotation before acting, then restores them at the end of the window. It creates and deletes no object, and it never touches kube-system, kube-public, kube-node-lease, argocd, flux-system or its own namespace. A workload annotated onicost.com/scheduler: ignore is left alone too.
Data hosted in France
The service and your data are hosted in France, with Scaleway, in the Paris region. Data is kept for 13 months. The credentials of your cloud accounts are encrypted at rest, and payments go through Stripe.
The privacy policy details the data processed, how long it is kept and your rights.
Access that fits your teams
Each member of an organization receives a role, and the Business plan adds OIDC or SAML single sign-on on your verified domains. You can apply your identity policy without separate accounts.
Report a vulnerability
Write to contact@onicost.com to report a vulnerability. The file /.well-known/security.txt publishes this contact in the standard format. The code of the agent Helm chart is public, so your team can review it before any install.
Frequently asked questions
Can the agent read my Secrets?
No. Its ClusterRole gives no access to Secrets or ConfigMaps, and the kubelet mounts the agent token.
Can I exclude a namespace?
Yes. The exclude.namespaces value of the chart drops everything from the listed namespaces before sending.
Where is my data hosted?
In France, with Scaleway, in the Paris region, for 13 months.